A Watershed moment in DPDPA Compliance

As Indian Data Fiduciaries try to find the ways to achieve DPDPA Compliance, the challenge stares at them. There is no precedence for them to follow. Even if they think GDPR is a good path, what is good for GDPR in EU may not be good for DPDPA in India. The law is different and the people are different. Hence a strategy for implementing DPDPA compliance has to find its own path.

FDPPI has found that Indian Banks are keen on DPDPA compliance and but are struggling to find the right path. Banks (like many other organizations) function at the branches but are Governed from the HO. Data exchange with the Data Principal happens at the Branch level where there is autonomy for collection, processing, disclsoure and grievance redressal. While the HO may set policies, implementation has to happen at the branch level.

SBI therefore is a conglommerate of 23000 branches where personal data of customers is processed. Any methodology for implementation and audit of DPDPA which does not recognize DPDPA compliance of the Bank as an aggregation of 23000 branch units is likely to be inefficient and unsustainable.

Implementation is the responsibility of the Banks. They may chose any path to reach the goal as it suits them.

But FDPPI and AIDAI have taken upon themselves to develop a system of Data Audit that is effective for Banks which have autonomous branch units where Personal Data is processed.

This is a combination of a “Standard for Compliance” and a “Standard for conducting Audits”.

Data Governance and Protection Standard of India (DGPSI) is already known to the market as the standard for DPDPA Compliance. Now AIDAI, (Association of Independent Data Auditors), a division of FDPPI has introduced a Standard Audit methodology named DA-SOP600 to enable independent audits at branch level to be aggregated at the enterprise level just as Statutory Financial audits udner ICAI guidlines under SA600 is handled.

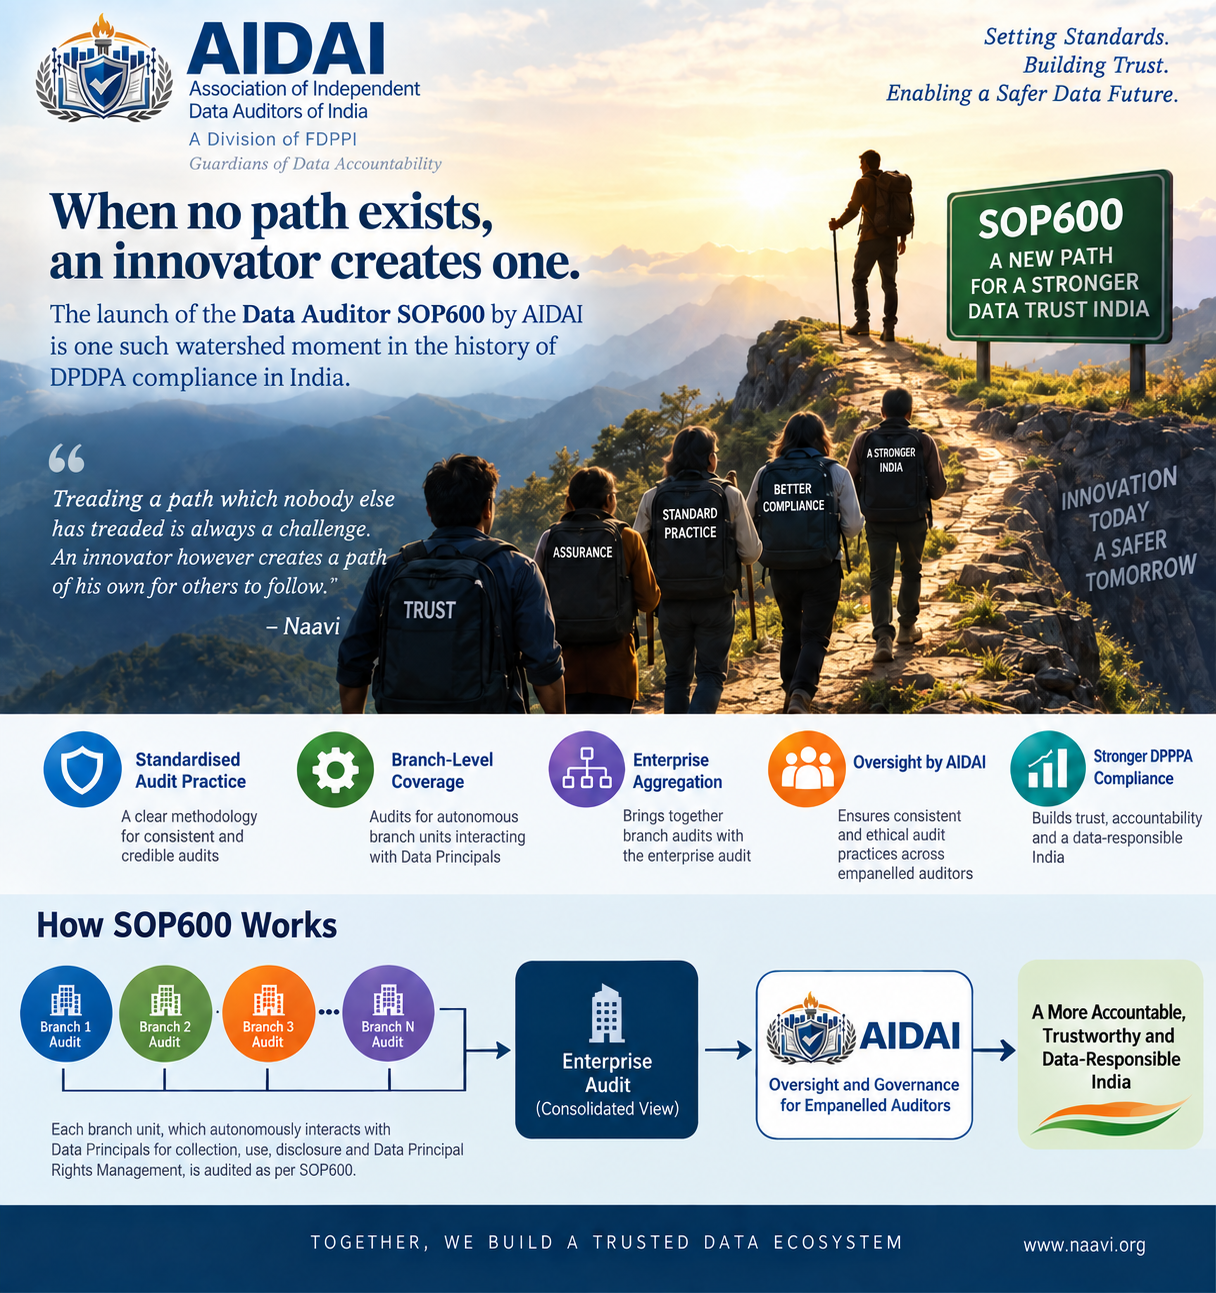
AIDAI’s SOP600: A New Path for Data Audit under DPDPA

The launch of Data Auditor SOP600 by AIDAI (Association of Independent Data Auditors of India), is a watershed moment in the history of DPDPA compliance in India. This has created the path for DPDPA compliance in Banking organziations In India which have customer interface at branch level, ATM level, Business Correspondent level etc.

It is said that SBI function with  23000+ branches, 63000+ ATMs, 82000+ Business correspondent outlets. All these are Personal Data Collection and Processing points which needs to be factored in for DPDPA compliance.

Banks like Canara Bank/PNB  may have  10000+ branches and other Banks may have lesser number of Customer interface points. But the scale of the problem is mind boggling.

How is it appropriate to consider SBI or any other Bank as a single Data Fiduciary where a single DPO will manage the compliance and a single Data Auditor will audit?

SOP600 is a solution which AIDAI has found for conducting Data Audits. But it also holds the key for compliance.

It addresses a practical problem that is likely to become increasingly important as organisations move from a centralised model of data governance to a distributed operational model, where individual branches, business units, departments and locations independently interact with Data Principals.

The Branch is Where Privacy Actually Happens

Much of the discussion around data protection compliance tends to happen at the corporate or enterprise level. Policies are framed at the Head Office, Privacy notices are approved centrally, Data protection officers and legal teams sit at the enterprise level. Technology controls may also be centrally designed.

But  the actual interaction with the Data Principal take place very often, at the branch. It is a point of data collection, data use, data disclosure and Data Principal interaction.

The DPDPA compliance posture of the organisation cannot therefore be understood merely by looking at what the Head Office says it does.

The Challenge of Distributed Data Governance

The idea behind Data Auditor SOP600 is significant because it attempts to establish a standardised audit approach for branch and sub-unit environments.

The objective is not to replace the enterprise audit.

It is to create a mechanism through which the activities of autonomous units can be examined systematically and then aggregated into the enterprise-level audit perspective.

This is a fundamentally different way of looking at data protection auditing.

Instead of asking only, “Is the organisation compliant?”, the auditor can progressively ask, “Are the units through which the organisation interacts with Data Principals following the prescribed data protection practices?”

And then:

“What does the combined evidence from these units tell us about the enterprise’s overall DPDPA compliance posture?”

That is a much more operational approach to data governance.

What is important to note is that this principle not only assists the Auditing but also gives a direction to the implementation team of how to implement the DPDPA Compliance.

The designation SOP600 itself is symbolic of the philosophy behind the initiative. The objective is not simply to create another Standard Operating Procedure. It represents an attempt to institutionalise a repeatable and scalable audit methodology.

AIDAI, as the Association of Independent Data Auditors of India and a division of FDPPI, has an additional responsibility in this ecosystem.

The purpose of an auditor is not merely to identify non-compliance.

An auditor must also operate within a framework that promotes:

    • consistency,
    • independence,
    • professional discipline,
    • evidence-based assessment,
    • repeatability,
    • accountability, and
    • ethical conduct.

SOP600, as part of the emerging AIDAI framework and its Code of Ethics, seeks to create such a common professional path for empanelled auditors.

This is important because the credibility of an audit ecosystem ultimately depends upon the consistency of the audit process.

Two auditors examining comparable environments should not produce dramatically different outcomes merely because they follow completely different methodologies.

Standard Operating Procedures help reduce such variability.

The Bigger Idea: Compliance Is Not a Head-Office Function

Perhaps the most important message emerging from SOP600 is this:

DPDPA compliance cannot remain confined to the legal, IT or privacy department of an enterprise.

It has to reach the operational edge of the organisation. The branch manager, The customer-service executive, The sales employee, The HR representative, The field officer, The person receiving the KYC document, The person responding to a Data Principal’s request, The person deciding whether information can be disclosed.

These are the people who convert a policy into actual behaviour.

Therefore, the effectiveness of the DPDPA framework ultimately depends upon what happens at the point of data interaction.

A New Dimension to Independent Data Auditing

Traditional auditing often follows a top-down model. The enterprise is examined as a single entity. SOP600 introduces the possibility of a bottom-up evidence architecture.

The auditor can examine the operational units and then build the enterprise picture from the evidence emerging from those units.

This does not eliminate the need for enterprise-level auditing. On the contrary, it strengthens it.

A Watershed Moment?

Whether SOP600 ultimately becomes a widely adopted industry practice will depend on how the framework is implemented, tested, refined and accepted by Data Fiduciaries and the professional community.

But its significance as an experiment in structured, distributed and aggregatable data auditing is difficult to ignore.

The initiative raises an important question for every large Data Fiduciary:

Do you really know how personal data is being handled at every operational point where your organisation meets a Data Principal?

If the answer is uncertain, perhaps the next generation of DPDPA audits will have to look beyond the Head Office.

The future of data protection assurance may lie not only in auditing the enterprise — but in auditing the enterprise through its operational units.

And that is the path that SOP600 seeks to create.

The Journey Has Begun

Treading a path which nobody else has trodden is always a challenge.  But an innovator does not wait for someone else to build the road. He creates the road. And once the road is created, others can follow.

SOP600 is one such attempt to create a new road for the Indian data protection profession.

The path is open.

Let the auditors walk it.

Let the Data Fiduciaries test it.

Let the profession improve it.

And ultimately, let the objective remain what it has always needed to be, A more accountable, trustworthy and data-responsible India.

Naavi
Posted in Privacy | Leave a comment

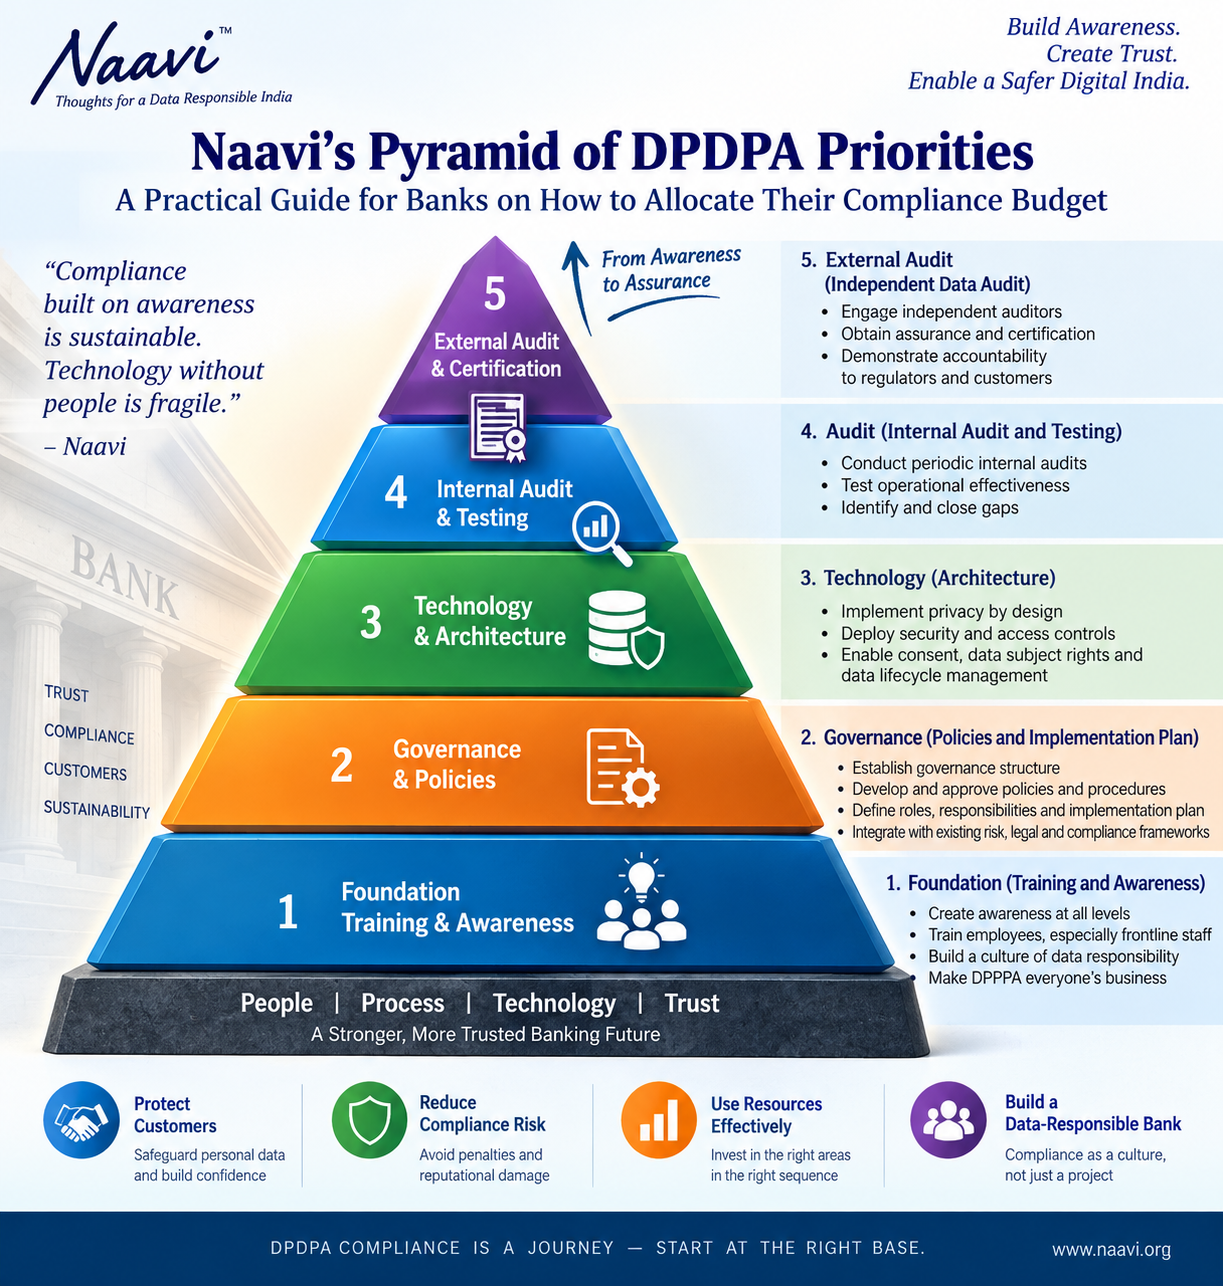
Attention : Chairmen of Banks… Review your priorities on DPDPA spending

Indian Banks are on a money spending spree to demonstrate their commitment to implementation of DPDPA. The Boards of the Banks appear to have not spared any effort to sanction budget for DPDPA Compliance.

But are the Banks spending their money wisely?

It appears that Banks are now investing their DPDPA budget mostly on purchase of software and in some cases hardware also. There is some investment on training and awareness but the level is very low when compared to the investments being made for IT.

DPDPA compliance is more of Governance than IT. Hence the prioritization of spending the DPDPA investment needs to be relooked by these Banks.

I urge the Chairmen of Banks and the Directors to review their proposed budget on DPDPA Compliance and check it against the above recommendations. This will a decision that is sustainable beyond your terms.

Naavi


Posted in Privacy | Leave a comment

For the attention of All DPDPA Auditors

Join a discussion on the new concept of DPDPA Audit for Banks … and other entities with multiple Data Processing units.

Naavi

Posted in Privacy | Leave a comment

FDPPI opens a new Vision of Data Audit

As part of the new developments in FDPPI, a new system of Data audit for large organizations involving multiple Branch units has been introduced.

Many major Banks like Canara Bank and SBI have already announced substantial investments in software for compliance. Many of them have also engaged the services of Big4 auditing agencies.

We are aware that neither the software companies nor the Big4 audit firms have fully integrated the concepts that FDPPI is proposing. They may also defend their current software or systems as adequate for organizations like SBI or Canara Bank.

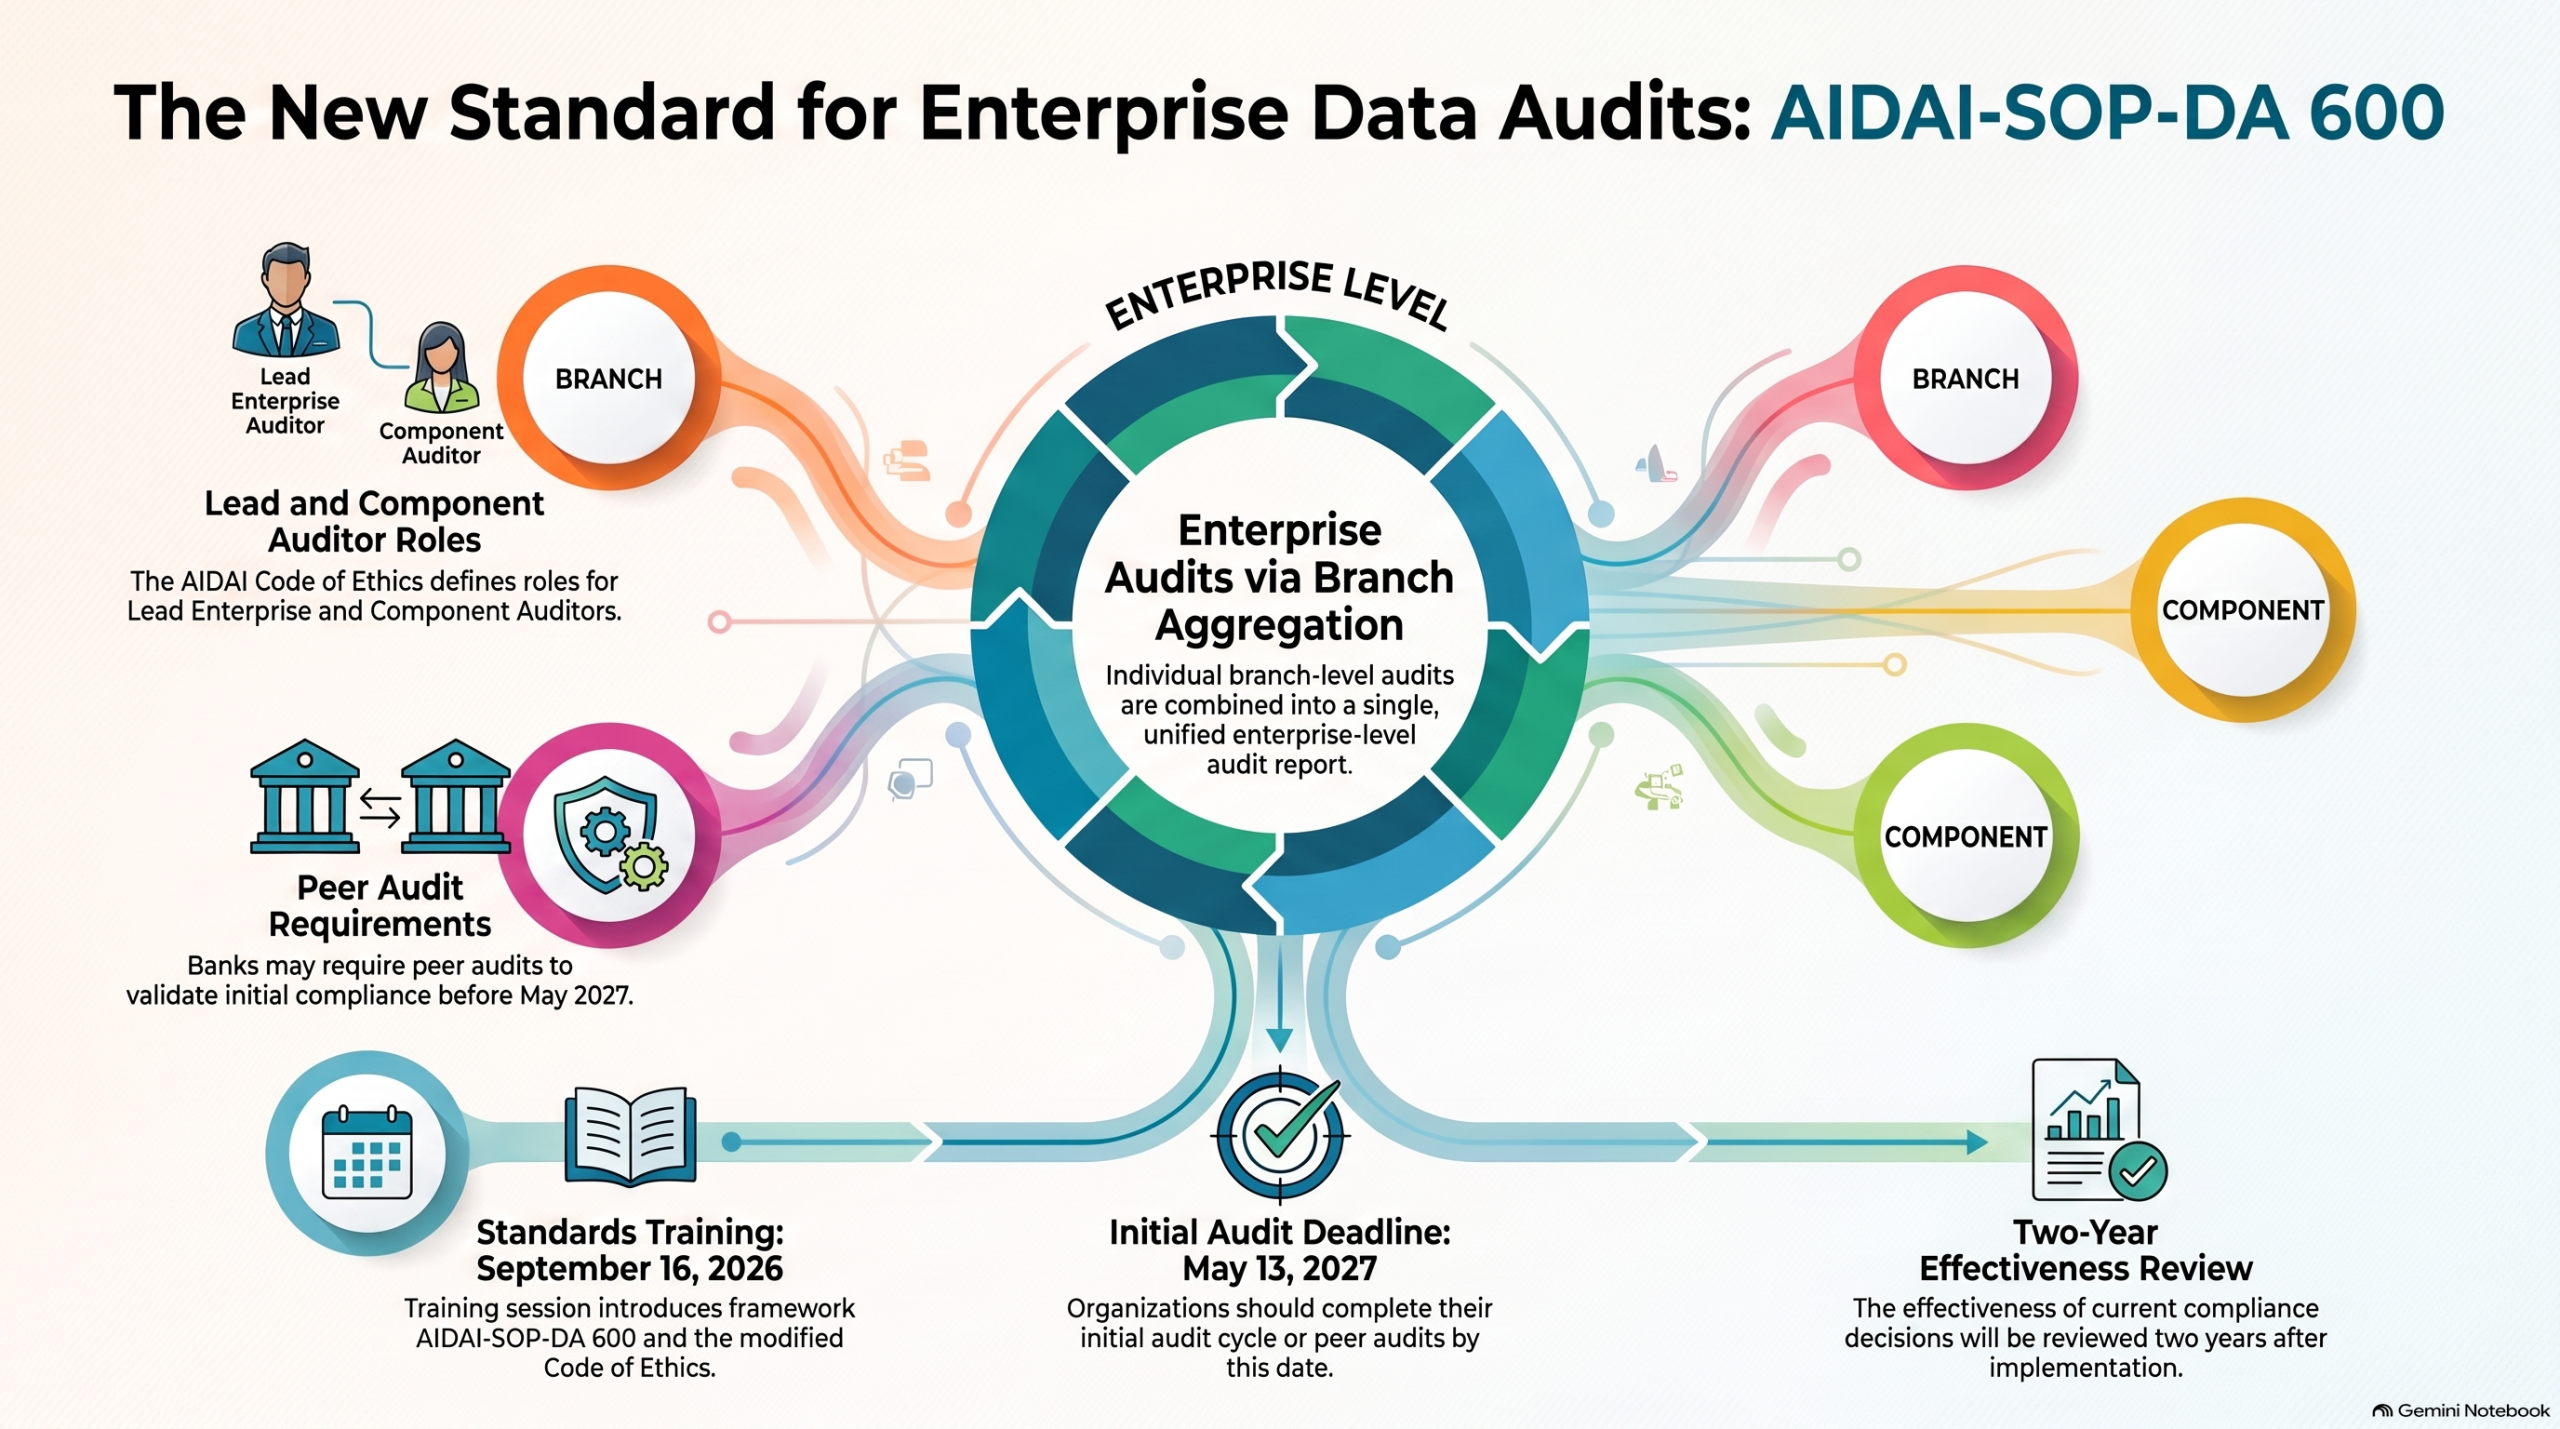
We at FDPPI have however decided that such enterprise level audits have to follow the model of  “Aggreagtion of Branch level Audits” . FDPPI has prepared its audit system for this purpose and introduced the standard procedures to make such audits to be conducted on a common standard and under a common organizational control of AIDAI.

AIDAI has actually published a new Code of Ethics for its empanelled Data Auditors which incorproates the principles of Lead Enterprise Data Auditor and Compenent Data Auditors.

We expect the Big4 to follow suit.

We hope the Banks posess the necessary knowledge to ask the right questions with their consultants to ensure that they are not finalizing compliance decisions solely because the audit is being performed by an organization which has large turnover. Going by some of the developments at NABARD and Bank of Baroda, it is difficult to be confident that there is a satisfatory level of understanding of the DPDPA problem at some of these Banks before they entered into multi crore contracts at public cost.

It will be after 2 years that we will be reviewing the effectiveness of the current decisions made by these Banks when customer complaints may  start showing up at DPB.

Many of these banks may require “Peer Audit” either before completing their exercise of initial audit before 13th May 2027 or there after.

AIDAI/FDPPI however believes that we need to build a strong army of data auditors who can undertake the audits of multiple compliance units which can be aggregated into an enterprise level audit.

We are also conducting a specific training program to introduce the framework AIDAI-SOP-DA 600 and the modified Code of Ethics in our special Jnaana Vardhini session on 16th September 2026.

These will be the standards for the future and defining the course of DPDPA Compliance in India.

Naavi

(Comments are welcome)


Posted in Privacy | Leave a comment

Implementation of DPDPA.. The priorities

Software is a necessary requirement of DPDPA compliance but neither it is sufficient nor the first priority.

Going by newspaper reports it appears that Banks in India are showcasing their DPDPA compliance by installing the necessary software and hardware to enable DPDPA compliance.

A report in Business Standard today indicates that SBI is targeting its compliance program to be completed by end of 2026, five months ahead of the due date for implementation. The report highlights that SBI has “Procured” software and hardware as part of its preparations for compliance and installation and deployment eis expected to be completed by Decmber.

Similarly, Canara Bank recently announced that it has awarded a contract of Rs 52 crores to a software company for DPDPA compliance.

While it is encouarging to note the large investments being committed and the desire to meet the deadline, it is not clear if Banks are adopting a path to compliance which is likely to lead them to a software dependent business model.

Most of the Banks have not completed their employee awareness program and now if they are already committing to the purchase of software, they are likely to encounter problems sooner or later when the dynamic industry needs to make changes.

Banks in India have a unique problem in DPDPA compliance since data processing occurs at hundreds of branches while the compliance may be focussed on the CBS system as if the Data Center is the unit of compliance.

What the Banks may be initially doing is to send out notices to all their current customers like the renewal of KYC and most of the investments may represent this cost. This is only one part of the requirement. What is more critical is the abilit to meet the Data Access Requests, Grievance redressal etc.

We need to be war of some of the Banking giants creating a wrong path to compliance and claiming that what they are doing only is the correct path.  It will require some complaints and enquiry by DPB and appeals at TDSAT and Supreme Court before their approach gets a validity.

Let us wait and see how things proceed…

Naavi


Posted in Privacy | Leave a comment

DGPSI-SOP600 an essential thought for Data Audits

The Digital Personal Data Protection Act, 2023 (DPDPA) recognizes a legal entity as a single Data Fiduciary or Significant Data Fiduciary. But in practice,  a large organization may have hundreds or even thousands of branches, subsidiaries, regional offices, functional divisions and operational units. Each of these units may independently collect, use, store, disclose and otherwise process personal data.

In such contexts, the legal entity may be one. The data-processing reality may be many.

This creates a fundamental question for the DPDPA audit:

How does an auditor audit one enterprise when the enterprise itself operates as a collection of autonomous data-processing units?

This is the question that has led to the development of DGPSI-SOP600, a proposed Standard Operating Procedure for conducting enterprise-level data audits where a Significant Data Fiduciary has multiple sub-units.

The concept of an Independent Data Auditor is going to become an important professional function in India’s emerging data protection ecosystem.

The Association of Independent Data Auditors (AIDAI), a division of the Foundation of Data Protection Professionals in India (FDPPI), has been created with the objective of developing this professional ecosystem.

AIDAI is working towards establishing professional standards under which individuals can be trained and certified as Certified Independent Data Auditors, capable of undertaking DPDPA compliance audits and related assignments such as Data Protection Impact Assessments and Algorithmic Audits.

The objective is not merely to create another certification. The larger objective is to create confidence in the audit process itself.

One enterprise does not necessarily mean one data environment

Consider a large bank. Legally, the bank may be one entity. Operationally, however, it could have thousands of branches. Each branch may interact with customers, employees, vendors and other individuals. Each branch may generate and process personal data through its own operational processes.

The same situation can arise in:

  • hospitals and healthcare networks;
  • universities and educational institutions;
  • insurance companies;
  • large retail chains;
  • manufacturing enterprises;
  • government and public-sector organizations;
  • technology companies with multiple business divisions; and
  • multinational organizations operating through regional entities.

Some of these units may perform relatively routine processing.

Others may undertake extensive or high-risk processing.

Some may themselves have characteristics that could potentially make their operations relevant to the determination of Significant Data Fiduciary obligations.

Yet the DPDPA compliance obligation ultimately has to be viewed at the level of the legal entity to which the law applies. This creates a practical audit problem. The Central Auditor cannot simply look at the corporate headquarters and conclude that the enterprise is compliant.

The auditor needs reasonable assurance that the data-processing activities occurring across the organization have also been appropriately examined.

The “Central Auditor – Sub Unit Auditor” model

This is where the concept underlying DGPSI-SOP600 becomes important.

The proposed model distinguishes between:

1. Central or Enterprise Auditor

The Central Auditor is responsible for the overall enterprise-level audit.

The Central Auditor has to understand:

  • the organization’s governance framework;
  • enterprise-wide policies;
  • common technology platforms;
  • central data-processing activities;
  • common vendors and processors;
  • enterprise-wide security controls;
  • HR and employee-data practices;
  • privacy notices and consent mechanisms;
  • data retention and deletion practices;
  • data principal rights management;
  • incident and breach management;
  • DPIA and risk-management mechanisms; and
  • the manner in which individual business units implement these requirements.

But the Central Auditor may not be able to personally audit every operational location.

A bank with 5,000 branches cannot reasonably expect one audit team to physically conduct a complete independent audit of every branch within the annual audit cycle.

2. Sub-Unit Auditor

The Sub-Unit Auditor undertakes the audit of an identified branch, subsidiary, regional office, functional division or other autonomous data-processing unit. The Sub-Unit Auditor works against a common audit standard. The findings are then communicated to the Central Auditor in a prescribed format.

The Central Auditor can therefore use the work of appropriately qualified and independent Sub-Unit Auditors as an input into the enterprise-level audit.

This is a mechanism for creating audit scalability without sacrificing standardization.

The importance of a common audit standard

There is, however, an obvious problem to be resolved. If 1,000 branches are audited by 100 different auditors using 100 different methodologies, the Central Auditor will receive 100 different interpretations of “compliance.”

The answer lies in standardization.

FDPPI has already been developing the DGPSI – Data Governance and Protection Standard of India framework, including sector-specific and functional standards such as DGPSI-Banks, DGPSI-Hospital, DGPSI-Education, DGPSI-HR and DGPSI-AI.

These standards provide a common vocabulary and a common framework for evaluating data governance and protection practices.

AIDAI proposes to build upon this foundation by establishing a common methodology for coordination between the Central Auditor and Sub-Unit Auditors.

Thus, the objective is:

Different auditors. Different locations. One audit language. One audit methodology. One consolidated assurance framework.

Why SOP600?

DGPSI-SOP600 is being conceived as the procedural layer that sits above the individual audit standards. The DGPSI framework can tell the auditor what should be examined.

SOP600 seeks to establish how multiple auditors should work together when the organization has multiple autonomous data-processing units.

Among other things, the SOP addresses the expected procedures for:

  • identifying the units that require separate audit attention;
  • determining the scope of sub-unit audits;
  • allocation of responsibilities between Central and Sub-Unit Auditors;
  • adoption of common audit standards;
  • communication between auditors;
  • reporting of audit findings;
  • treatment of deficiencies identified at sub-unit level;
  • escalation of significant findings;
  • reliance by the Central Auditor on Sub-Unit Auditor reports;
  • consolidation of findings;
  • documentation of the basis of reliance; and
  • preparation of the final enterprise-level audit report.

The detailed standard is currently under development and will be subjected to review by the Governance Body and Advisory Group of AIDAI/FDPPI.

Independence is not enough

There is another important principle behind this initiative.

The word “independent” in the context of an auditor cannot be reduced merely to the question:

“Is the auditor an employee of the organization?”

Professional independence has a much wider dimension.

The Central Auditor must have confidence that the Sub-Unit Auditor has conducted the assignment objectively. The Sub-Unit Auditor must have confidence that the methodology being followed is consistent with the enterprise audit methodology. The organization must have confidence that different auditors are not applying different standards merely because they have different professional backgrounds.

And ultimately, the Data Protection Board and other stakeholders must be able to place reasonable reliance on the integrity of the audit process.

Therefore, AIDAI’s role as a professional self-regulatory body becomes significant.

Self-regulation as a professional responsibility

AIDAI is not presently a statutory regulator. Nevertheless, a professional body can contribute significantly to the development of professional discipline.

Through:

  • common standards;
  • auditor training;
  • certification;
  • empanelment;
  • ethical requirements;
  • quality expectations;
  • peer review;
  • professional guidance; and
  • appropriate disciplinary measures,

a professional ecosystem can be created in which an auditor’s professional reputation becomes an important component of independence and accountability.

Empanelment can also provide an institutional mechanism for dealing with serious deviations from professional standards, including suspension or dis-empanelment where appropriate.

This is similar in principle to how other professional audit ecosystems have evolved around common professional standards. The objective is not to create bureaucratic control over auditors. The objective is to create trust in the audit profession.

Can the Central Auditor “rely” on another auditor?

If a Central Auditor relies upon the audit conducted by a Sub-Unit Auditor, the Central Auditor cannot simply say:

“The branch has been audited by another auditor, so I have no responsibility.”

At the same time, it would be impractical to expect the Central Auditor to repeat the entire audit conducted by every Sub-Unit Auditor. There must therefore be a structured basis for reliance.

The Central Auditor needs to know:

  • Who conducted the sub-unit audit?
  • Was the auditor appropriately qualified and independent?
  • What standard was followed?
  • What was the scope?
  • What evidence was examined?
  • What exceptions were identified?
  • Were significant deficiencies escalated?
  • Was the audit completed according to the prescribed methodology?
  • Were there unresolved disagreements?
  • Can the Central Auditor place reliance on the conclusions?

SOP600 seeks to provide the procedural architecture for answering these questions.

The financial audit analogy

The financial audit profession has already faced a similar scalability challenge. Large organizations cannot always be audited by one team examining every transaction and every location personally.

Professional standards and structured audit methodologies allow auditors to work with component auditors and rely, subject to appropriate procedures, on work performed at different components of an organization.

The data protection audit profession can learn from this experience. But there is an important difference namely that  a data audit involves governance, technology, people, contracts, processes, algorithms, security controls and the rights of individuals. T

herefore, the audit methodology has to evolve specifically for the data environment. SOP600 is an attempt to address precisely this emerging requirement.

From “audit of the organization” to “audit of the data ecosystem”

Perhaps the biggest conceptual change is this is that the DPDPA audit cannot remain a headquarters exercise”

The real data governance of an enterprise exists wherever personal data is processed.

The branch employee who collects KYC information.

The hospital employee who accesses patient records.

The HR department processing employee information.

The AI system making decisions based on personal data.

The outsourced processor handling customer information.

The regional office maintaining local records.

All of these are components of the organization’s data ecosystem.

Therefore, enterprise-level assurance must ultimately connect the governance at the centre with the processing at the edges.

DGPSI-SOP600: Building the bridge

DGPSI-SOP600 is being developed as a bridge between these two realities. Enterprise-level legal responsibility and distributed operational data processing.

The principle is simple “Central accountability does not mean centralized processing”.

And therefore, “Enterprise-level audit must be capable of absorbing distributed audit evidence.”

AIDAI’s objective is to create a system in which a Central Auditor can coordinate with qualified Sub-Unit Auditors, use a common methodology, evaluate their work, and consolidate the results into a credible enterprise-level DPDPA compliance assessment.

The challenge is substantial.  India is creating a new data protection regime. Along with it, India also needs to create the professional infrastructure that can make compliance assurance credible, scalable and trustworthy.

DGPSI-SOP600 is one step in that direction.

The detailed standard is presently under development and will be reviewed by the Governance Body and Advisory Group of AIDAI/FDPPI before its finalization.

The objective is not merely to produce another SOP. The objective is to build an audit system that can match the scale and complexity of India’s data-driven enterprises.

Naavi

(Comments are welcome)


Audio Overview

Video Overview

Posted in Privacy | Leave a comment