Today, 13 November 2026, the DPDP Rules 2025 complete one year since notification. In about six months, in May 2027, the main obligations of the DPDPA 2023 will kick in for every Data Fiduciary in the country.
Now the website www.dpbi.in is active and the first milestone in the implementation of DPDPA has been reached.
DEPA for AI Training: are the priorities right?
Currently the discussion has shifted to the Data Empoerment and Protection Architecture for AI training on which a handbook was released recently.
This DEPA-AIT architecture has opened up a new area of discussion on how it affects DPDPA implementation and whether it would help development of Indigenous AI models.
Who will own the value of Indian data?
The DEPA framework is meant to make datasets available for AI training through a structured and secure system. But it is not confined to Indian AI developers. The participants include AI developers, researchers, startups and “enterprises”, and the draft lays down no clear Indian ownership or control condition for any of them.
These datasets come from Indian hospitals, banks, educational institutions and public bodies. They are the product of years of institutional work and investment, and some of them were created with public money.
DEPA-AIT needs to answer at least four sovereignty questions:
- Access: Who is allowed to access and use Indian datasets?
- Derived assets: Who owns or controls the models, weights and other IP built from them?
- Commercial benefit: Who earns when those models are deployed globally?
- Onward use: Can the models or derived datasets be passed on to overseas affiliates or third parties without Indian oversight?
The draft’s emphasis on secure data environments is welcome. But technical security does not answer any of these four questions.
Remember CIBIL
We would like to recall the earlier incident of CIBIL and how the control on massive amount of sensitive data held by the company was quitely shifted to a foreign commercial entity like Trans Union. The instrument that enabled collection of the sensitive data was a law namely the Credit Information Companies (Regulation) Act, 2005 (CICRA).
Under CIRCA, Section 15, the Act and the Reserve Bank of India (RBI) guidelines mandate that all credit institutions (banks, cooperative banks, and NBFCs) must join and report data to all registered Credit Information Companies (CICs).
Under Section 17, CICRA legally empowers CICs to collect credit information from their member banks and furnish it to authorized specified users.
Because sharing consumer credit and repayment data with credit bureaus is a statutory obligation mandated by law rather than a contractual choice, individual customer consent is legally unnecessary for mandatory credit reporting.
Initially CIBIL was owned by Indian Banks to the extent of 90% and the mandate was acceptable. Subsequently TransUnion was allowed to acquire 90% share holding of CIBIL, which is now renamed as TransUnion CIBIL. The total cost of acquisition is estimated to be about rs 3809 crores.
According to Google 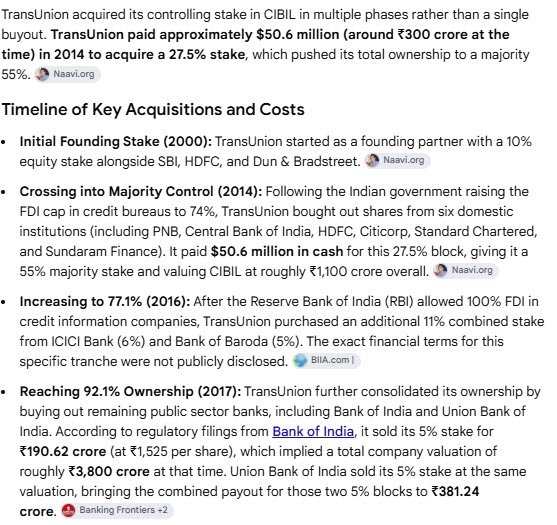
CIBIL-TransUnion episode has indicated that an institution can be set up in India, operate under Indian law and handle Indian data, and yet have its ownership, strategy and commercial direction decided by a foreign corporation.
A similar thing is likely to happen in the AI Training domain also. Access to nationally valuable datasets may pass on under the DEPA for AIT structure to agencies outside India with the intelligence and economic value built from them. CIBIL should teach us to think ahead, before such ownership arrangements become impossible to reverse.
A suggestion: accredited Indian Data Training Companies
Our suggestion is that DEPA-AIT should have been built in a more structured participation model.
Indian data providers could have been enabled participation only through accredited Indian Data Training Companies, which operate under clear eligibility, security and accountability requirements. These companies would then act as a protective layer between the original data providers and the AI developers who want access.
Eligibility should have rested on a proper “Fit and Proper” test covering beneficial ownership, control, security practices, jurisdiction and the ability to comply with Indian regulation.
The framework should also lay down clear rules on:
-
- ownership and licensing of models built on Indian datasets
- access to model weights and derived datasets
- restrictions on unauthorised onward transfer
- audit rights and regulatory access
- benefit-sharing with the original data providers
- special conditions for datasets created with public money or belonging to strategic sectors
India should be a partner in the value created, and not just a supplier of raw material to the global AI industry. Otherwise we may end up in a situation where India provides the data, foreign entities own the intelligence, and Indian institutions later pay to use capabilities built largely from their own data.
That is how data colonies are created in the digital age. We need to settle this now, before the architecture goes live and the institutional arrangements harden.
MeitY wears two hats
There is a deeper institutional issue here.
MeitY is responsible for promoting India’s IT industry, driving AI adoption and building a competitive digital economy. The same Ministry also frames and administers the regulatory framework for the digital world, including the ITA 2000 and the DPDPA 2023.
The two roles pull against each other when promoting a technology starts to take precedence over the safeguards needed to adopt it responsibly. AI development and data protection may move together, but promoting AI cannot become a reason to delay an effective data protection regime.
Perhaps it is time to consider separating the promotion of the digital industry from its regulation. The Ministry of Law could play a larger role in keeping the law coherent, and an independent, adequately empowered body could handle regulation and enforcement of digital and data protection obligations. This would leave MeitY free to promote technology while keeping regulation out of the shadow of promotion. It is a reform question for the highest levels of Government.
In the last month MeitY has started holding public awareness meetings on DPDPA. These are welcome, since organisations, professionals and citizens all need to understand the law. But these need to be followed up with the DPB being fully operational with the Chairman and the Members taking charge.
An appeal to the Minister and the Prime Minister
DPDPA is a commitment to protect the personal data of every Indian citizen. Making it work needs much more than notified rules: a functioning Data Protection Board, a working Consent Manager ecosystem, trained professionals, and Data Fiduciaries who understand their responsibilities.
At the same time India is building an ambitious architecture to make datasets available for AI training. That should not go ahead without a clear policy on data sovereignty, Indian institutional control and fair sharing of the economic benefits.
India can build a globally respected data protection regime and a strong domestic AI ecosystem at the same time, provided we pursue both with the national interest clearly in view. And let us make sure the value created from Indian data stays within reach of Indian institutions and Indian regulators.
Naavi
P.S: Yesterday, the DPBI website became operational during the day. It was not open in the morning and hence the original version of the above article had some comments on the delay. These have been removed now.