Voluntary Special Interest Group on Secure Digital India (VSIG-SDI)

 Regular visitors of this site remember the article “If NAMO is the CEO of Digital India, who is the CISO”?

This thought is still ringing in the minds of many of us who are wholeheartedly supporting the Digital India project but frequently expressing adverse comments on many policy initiatives of the Department of Electronics and Information Technology” (DeitY).

A few days back a group Information Security Professionals in a WhatsApp group came together with a thought that Government of India is going ahead with its Digital India project without an appropriate Information Security back up and we need to do something to contribute our thoughts on how to change things for the better.

With this idea, the group decided to promote what can be called a “Voluntary Special Interest Group on Secure Digital India and start deliberating on how to progress further.

In order to collaborate with the persons of similar interest, a Facebook page was opened at www.facebook.com/securedigitalindia.

As a thought starter, I had placed a PPT on the initial thoughts I had shared it with the members of the group. Now I find that I am getting requests from many on this PPT which is only an information on the proposed activities of this group. We are yet to come up with any documents containing suggestions which can be shared with the public. We hope to do the same in due course.

However, since it is difficult to handle individual requests for the sharing of the document, I am placing the current version of the document on this website.

The document is available here

I welcome comments. Comments can be posted as visitor’s comments on the facebook page or here on naavi.org. You can also communicate with Naavi on his email.

I also welcome any detailed white papers that can be published on naavi.org that would go with the objective of the group. This SIG and its activities is a voluntary activity of  a virtual group of IS Experts who we believe may be able to collectively provide recommendations to the DeitY which would be useful. Success of the thought is in your hands. Participate in full.

Naavi

Posted in Cyber Law | Leave a comment

Cyber Insurance and Data Breach Liability

In US it is stated that 46 of the 50 states have made Data Breach Notification mandatory. As a result when a data breach even occurs the company needs to conduct an in house audit and then send out notifications to all its customers who are likely to have been affected by the breach.

The cost of such notification itself is huge since in most cases the number of data lost runs to millions.

This data breach notification is recognized as one of the key drivers to the Cyber Insurance industry in US since these costs of data breach notification is a clear cash outgo for the company to be incurred almost immediately after a data breach comes to its knowledge.

Related Article in Computerweekly.com

In India, many companies are ignorant about whether there is any data breach notification obligation. Presently under Section 79 of ITA 2008, data breach incidents need to be reported to IN-CERT, though this is rarely observed and CERT-IN.

There is still however no specific obligation to notify the customers unless this is introduced as a part of the Section 79 notification on due diligence.

Recently Indian Press reported that two companies in Mumbai suffered extortion threats after some hackers threatened to reveal some illegal activities of the companies. This was also an incident of security breach in the company though we donot know if there was any customer information involved in the breach.

But  public do not know if this was reported to IN-CERT. In fact the Press have been helping the companies to keep their identity under wraps which also means the crime is kept under wraps.

Sooner or later the situation will change and data breach notification will become mandatory in India. Companies need to be prepared therefore for meeting the liabilities both in terms of costs involved in setting things right, notifying parties and also meet third party liability claims.

It is time they start asking themselves where they stand in this respect since some of these companies are also filing declarations under clause 49 of SEBI rules on listing which is similar to SOX guidelines.

Naavi

Related Article: Reddit.com

Posted in Cyber Law | Leave a comment

Protect Bank Consumers from Frauds or be prepared for disaster..A warning to BJP Government

Naavi has been arguing from a long time that Banks are vicariously liable for Cyber Crimes in which customers lose money. It is under this argument that in the S.Umashankar Vs ICICI Bank case, the adjudicator of Tamil Nadu held the Bank liable. Subsequently, Mumbai adjudicator came to the same conclusion in several cases.

Now I am glad that more people are echoing the same view. Here is a good article on the subject in Indian Express written by an IPS officer Mr Arun Bothra. (See article here).

Mr Bothra has rightly argued that in case of ATM and other Bank frauds, it is the failure of Bank’s security systems that should be recognized and held responsible.

(Naavi has placed his arguments in detail in many articles in this website and one can find these articles if a search is made within the site. Or click here).

However, cyber crime victims who have tried to prove their case in a judicial system have been repeatedly frustrated by the powerful Banks as the following developments indicate.

  1. The Chennai Adjudicator Mr P W C Davidar who held ICICI Bank responsible in several cases was transferred out of the department as soon as Ms Jayalalitha took over as CM. Subsequent adjudicators have not made any moves to hear further cases.
  2. The Mumbai adjudicator who decided many cases against Banks was transferred to Delhi by the current BJP establishment and since then Mumbai adjudication system has gone quiet.
  3. In Bangalore where two cases came up before the Adjudicator, he went a step ahead of the others by declaring that no case can be filed against a Bank under Section 43 of ITA 2000/8 since Bank is a “Company” and the section applies only to a “Person”.
  4. The Cyber Appellate Tribunal which ought to hear appeals against adjudications has been literally shut down since the Government both in the earlier regime under Kapil Sibal and the present regime under R S. Prasad are unwilling to appoint a chair person since 2011.
  5. Karnataka High Court is reluctant to intervene for reasons better known to it.
  6. The IT Ministers, PMs, Presidents and the CJIs in the last several years who have come and gone or are presently in charge have all been contacted by the undersigned and none of them have been able to get the Cyber Appellate Tribunal functional.

All this indicates that there could be a huge conspiracy to deny the Cyber crime victims in Banks from getting justice through the system.

Mr Modi and the BJP Government who are tying to push through the Digital India agenda are unable to ensure at least the presence of a Cyber Judicial System though we understand that  they cannot guarantee justice in the end.

The situation is very depressing and would qualify for a low rating of the country in Cyber Security Index or Human Rights Index.

Now more frauds are getting reported from the new generation banking systems and RBI is not even bothered to collect the right statistics nor force the Banks implement  the RBI guidelines either on Cyber Insurance or on Information Security.

Mr Arun Jaitely as FM as well as Mr Raghuram Rajan as Gov, RBI  donot seem to have any appreciation for the plight of the E-Banking customers and are busy with inflation control, fiscal deficit control, re-capitalization of Banks to meet Basle III norms, re-engineering the NPA figures etc. Both of them are unmindful of the possibility that once the frauds cross a critical level, Bank customers would shun E Banking and start using cash once again as the medium of exchange. There could be a run on the Banks and the Indian Banking system may collapse.

Yesterday I was having a discussion with Ms Melissa Hathway the Cyber Security expert in USA who has worked under both presidents George Bush and Obama and found out that she does not trust E Banking and prefers not to use it.  On the other hand in India our regulators who donot even understand the risk of E Banking neither try to correct the system nor leave it to the discretion of the public to use E Banking or stay outside. The Government by policy imposes public to mandatorily use E Banking for Tax Payment, Direct Benefit Transfers etc and literally throws the citizens to the cyber criminals laps.

I have already brought to the notice of Mr Modi that if he does not introduce Cyber Insurance to protect the users of E-Banking/E-Governance, the Digital India program is under threat and may come down like a pack of cards one day. I am still waiting for him to read and understand the import of what I am saying.

I also draw the attention of these politicians and regulators the enclosed video which covers a recent debit card fraud scam busted (partially) in Bangalore. In particular I want them to see how people are feeling that “Plastic cards are not safe” which is an indictment of the system of E Banking.

It gives them some idea of how rampant is Bank frauds and why the statistics of RBI on Bank frauds is completely unreliable and why RBI and even the Government schemes may be more handy for Cyber Criminals rather than the public.

See the video here

I hope Mr Bothra’s article appearing prominently in Indian Express of 1st October 2015 will open the eyes of Mr Modi despite his busy schedule in Bihar.

Naavi


Posted in Cyber Law | 1 Comment

Are We Cyber Ready?.. Melissa Hathway Shares her concerns

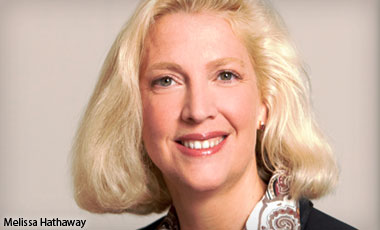
melissa_hathawayMelissa Hathway, the Cyber Security expert from US was in Bangalore recently and addressed members of DSCI Bangalore Chapter at NLSUI on 1st October 2015.  Melissa was until recently working with US President Obama and was tipped to be appointed as the “Cyber Czar”. She also worked as Director of the Joint Inter agency Cyber Task Force during President George Bush time and brings with her enormous US and International experience in management of Cyber Security at the Government level. She however left the US Government post and is now working as an independent Cyber Security Consultant.

During her presentation, Ms Melissa traced in detail how in the emerging Digital World, people are connected amongst themselves and with machines and machines themselves are connected with other machines, people and machines are connected with the house and the environment etc. and the security  issues emerging therefrom.

Speaking on the privacy issues, she raised a pertinent point that the risk to individual privacy from private sector enterprises such as Google is much more than from the Government agencies.

While hinting that National Security should get the priority in designing the IT infrastructure, she raised a question on whether all the connectivity we are thinking of in the IOT concept is at all necessary.

Another important point she made is to question the manufacturers of appliances on whether the electro mechanical engineers who design the new systems and freely put in IP devices to monitor the activity of the machine understand the “Risks” inherent in such connectivity.

She concluded her interesting and authoritative presentation with a very pertinent question which was not specific to India but was nevertheless relevant. The question was “Are we Cyber Ready”?

The talk was followed by a Q&A session in which as usual solutions were discussed in the form of how to build awareness among the masses on Cyber Risks, what should be the responsibility of the Telecom companies, whether the legal system is resilient, whether our law enforcement had the requisite knowledge? etc.

The undersigned left a question with Ms Melissa and the audience that while creating awareness of Citizens, Police and Corporate officials  is feasible, the biggest challenge was to create awareness in Judiciary and Top level Bureaucrats because they insulate themselves from attending any training sessions. She agreed that it was a challenge and it does exist in other countries also and strategies need to be found to bridge this lacuna.

Overall, it was a fruitful discussion and the audience felt that it opened new thoughts on security in the context of India entering the Digital India program.

Naavi

Related Info:

Cyber Readiness index 1.0

Cyber Readiness index 2.0

Cyber Security indicies-ITU

Posted in Cyber Law | Leave a comment

Why Cyber Insurance seekers need to do better home work

Naavi has been advocating that companies need to start using  Cyber Insurance in India though the current level of awareness as well as the penetration is low.

In these circumstances, the news that BitPay, a Bitcoin processor  could not recover its claim for a loss of $i.8 million despite having a Cyber Insurance policy since their claim was rejected by the Insurance company is disturbing.

At the same time, the incident highlights how lot of care is required before a Cyber Insurance policy is purchased and the purchaser should be able to analyze the policy terms in detail and avoid the kind of technical interpretations that were used by the Insurance Company in this case to reject the claim.

The details of the incident as reported in networkworld.com indicate as follows.

BTC Media had obtained a “Commercial Crime Insurance Policy” for $ 1 million from MBIC which stated

” “will pay for loss of or damage to ‘money,’ ‘securities’ and ‘other property’ resulting directly from the use of any computer to fraudulently cause a transfer of that property from inside the ‘premises’ or ‘banking premises’: a. To a person (other than a ‘messenger’) outside those ‘premises’; or b. To a place outside those ‘premises,’ “

In December 2014, the CEO of the company was spearphished the company’s CFO and managed to get hold of his email credentials. This was used to spoof mails to the CEO and 5000 bitcoins worth $1.8 million were stolen.

The Company filed a claim under the Cyber Insurance policy which was declined for the following reason.

““The Policy requires that the loss of money be the direct result of the use of any computer to fraudulently cause a transfer of that property from inside the premises to a person or place outside the premises. ‘Direct’ means without any intervening step i.e. without any intruding or diverting factor. The Computer Fraud Insuring Agreement is only triggered by situations where an unauthorized user hacks into or gains unauthorized access into your computer system and uses that access to fraudulently cause a transfer of Money to an outside person or place. The facts as presented do not support a direct loss since there was not a hacking or unauthorized entry into Bitpay’s computer system fraudulently causing a transfer of Money. Instead, the computer system of David Bailey, Bitpay’s business partner, was compromised resulting in fictitious emails being received by Bitpay. The Policy does not afford coverage for indirect losses caused by a hacking into the computer system of someone other than the insured,”

Bitpay has now sued MBIC for breach of contract, bad faith, failure to pay and statutory damages and seeking $950,000 in damages plus court fees.

The litigation is likely to go for some time and in the mean time the industry will debate whether Cyber Insurance is reliable at all.

MBIC may be technically correct where as BitPay may feel that MBIC has misrepresented and cheated. The argument could be based on the nature of contract and what is implied and what is not.

The incident highlights one of the points I have been highlighting for a long time and that is that a company obtaining  Cyber Insurance Contract must be able to decypher the policy terms and map it to the risks against which it needs a coverage. Any ordinary information security professional would list “Phishing” of credentials of any authorized user as one of the threats that can manifest into a risk and result in losses. He would presume that “Cyber Crime Insurance” will cover this. But being a technical person and not able to understand the terminology used in the contract which distinguishes “Direct” and “What is not Direct” as also “What is a loss” etc., he is unable to find out what the policy is really covering or not. While the CFO or even the legal department is able to understand this part, they may not know the anatomy of all Cyber threats. Thus neither the CFO/Legal team nor the IS team understands the nature of this “Techno Legal Contract” leading to problems of this nature.

Naavi and his group of professionals who are working on the India Cyber Insurance Survey will find out the views of the professionals in this matter and present it to the public shortly. (If you still want to participate and provide your feedback, rush to https://fs22.formsite.com/SBYrSa/form2/index.html)

CEOs and CFOs  should realize that all Cyber Insurance contracts are considered contracts of utmost faith and it is the responsibility of the proposer to disclose what risks he wants to be covered and ensure that the Insurer has not excluded the risks that he requires to be covered in the policy document. This requires the company to take the advise of a suitable consultant on his behalf other than the Insurance Company representatives and also the broker who is more inclined towards the Insurance company than the insured or is not fully conversant with all the legal nuances.

If proper care is taken then the kind of problem that BitPay is now facing should not have arisen.

Naavi

Related Articles:

networkworld.com

ibamag.com
Posted in Cyber Law | 2 Comments

Brand Ambassador of Digital India Program wins the International Award….

The officials at the Department of Electronics and Information Technology (DeitY) must be congratulating themselves on the excellent work done by their search committee  which found out and recommended  Sri Ankit Fadia to be appointed as the Brand Ambassador for the Digital India Program when they hear that their golden choice won an International award recently in a conference called DEFCON-23. The award was called “Security Charlatan of the year”.

It is great news that  Mr Ankit Fadia the celebrated Brand Ambassador for Digital India appointed on 1st July 2015 under a grand certificate  signed by none other than the then Secretary of the department Mr Ram Sewak Sharma won the coveted global award in the conference.

DEFCON-23 was held in Las Vegas between August 6-9 and I am not sure if any representative from DeitY  attended the.  But they must be glad to know that this is an annual event  widely attended by the community of “Hackers” from around the world and is very popular in the Information Security Community. Perhaps they should plan to attend the next DEFCON conference is expected to be  held between August 4-7, 2016 at Las Vegas.  As custodians of Digital India,  it will be a great opportunity for them to  identify more Brand Ambassadors for Digital India program.

(P.S: We can for the time being ignore the controversy surrounding the appointment  as to whether it  was done by the Secretary without the knowledge of others in the department and hence was  disowned in a PIB press release in the morning of 29th September 2015. However, by that time Mr Ankit had already published the certificate signed by Mr Ram Sewak Sharma and hence the department was forced to confirm the appointment  in the evening. See details).

The Best Security Charlatan award was won by Ankit Fadia against stiff competition involving 7 global nominations including one more from India namely Rahul Tyagi. The citation is available in the enclosed Video available on Youtube (See minutes 31 onwards.. It is a must watch). The award was given in absentia since Mr Fadia did not attend the conference.

If I stop here, the officials of DeitY will perhaps pat their backs and also hold a grand function in Delhi to honour their newly appointed Brand Ambassador. Because I donot want Mr Ravi Shankar Prasad and Mr Modi to be again facing inconvenient questions from the press, I would like to add the full details of the award.

The award is known as the “Security Charlatan Award” and is given for the “Best Charlatan in the Information Security and Hacking domain” as nominated by a global audience and voted during the conference.

The word “Charlatan” is not a commonly used word and hence we need to look up a dictionary for understanding the meaning.

According to dictionary.com, the word “Charlatan” means

 a person who pretends or claims to have more knowledge or skill than he or she possesses; quack.”

This was surprising for me since I wase looking at the “Brand Ambassador” of Digital India and confused how can he be a “Quack” and that too an award winning “Quack”?

Then I made a fresh search in the trusted Google and was horrified to get the meaning as

“A charlatan (also called swindler or mountebank) is a person practicing quackery or some similar confidence trick in order to obtain money, fame or other advantages via some form of pretense or deception.”

I was stunned..What? “also called swindler”?.. I intend taking up this with Mr Sundar Pichai and seek a clarification.

Anyway readers may check their own dictionary and confirm if this word has any different meaning.

If Mr Ankit Fadia is a global award winner for the “Security Charlatan” in the DEFCON conference, it is high time DeitY should check what kind of award their search committee should get for identifying and appointing a “Charlatan” as a “Brand Ambassador”.

May be our readers have a recommendation?..If so forward it to Mr Ravi Shankar Prasad.

Naavi

Posted in Cyber Law | 9 Comments