DPDPA is Here
Countdown to 13th May 2027
Google_site_search
Bing_site_search
-
Ask Vishy, the personal AI-assistant of Naavi for all your information on Naavi.org
-
-
-
Naavi
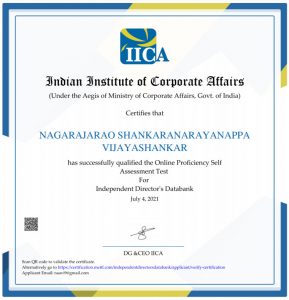
IICA Qualified Independent Director
-
-
DGPIN: 4PJ-7T8-FK8P: 12.94018310,77.55421020
-
Plus Code : WHR3+3P
-
Recent Posts
Archives
Archives by Date
-
-
Author Archives: Vijayashankar Na

3.84 lakh Aadhar cards cancelled
UIDAI has reportedly cancelled about 3.84 lakh Aadhar registrations done under “no finger print category” recognizing widespread fraud in the creation of the IDs. Money spent on these registrations in the form of commissions paid by the Government is a … Continue reading
Posted in Uncategorized
Leave a comment
Cyber Demonstration
The incidents in Delhi over the past one week have indicated how the power of the voice of the people can make even the most adamant Government to sit up and take notice. Initially the Government tried to ignore the … Continue reading
e-authentication framework for Government projects
The Department of Electronics and Information Technology, GOI (DeitY) has released a document called “e-Pramaan: Framework for e-Authentication”. This is intended to serve as the guiding document for all Central and State Ministries, departments and government agencies for implementing an … Continue reading
Posted in Cyber Crime, Cyber Law, Information Assurance, Privacy
2 Comments
Government is on a holiday
The Lieutenant Governor of Delhi who was enjoying a holiday in US while the city was burning has now come back to India. Many hope that there will be some accountability for what happens in Delhi now. People have criticized … Continue reading
Stealing Credit Card information from POS
Stealing of Credit card information when used on the Internet is a known vulnerability. It had also been observed that certain criminals had bought credit card information by bribing the employees of merchant establishments or by stealing the POS swiping … Continue reading
Posted in Cyber Crime
Leave a comment
Vulnerabilities in human space
According to NIST (National Institute of Standards and Technology), a “Vulnerability” in Risk Analysis context is defined as a”flaw or weakness in system security procedures, design,implementation, or internal controls that could be exercised (accidentally triggered or intentionally exploited) and result … Continue reading